

Managed XDR for Microsoft Security
Refoundry MXDR is a 24×7×365 agentic Security Operations Center that runs on your existing Microsoft Defender XDR, Sentinel, and Security Copilot investment. AI agents triage and investigate every incident in real time, and our SOC operators move from detection to containment in minutes - not days.
What Is Managed XDR (MXDR) and Why Does the Mid-Market Need It?
Growing companies face the same threats as global enterprises - identity compromise, automated lateral movement, cloud-based exploitation - but rarely have the same security bench. And the alerts never stop.
Most traditional managed detection services stop at detection: they hand you a ticket, and the attacker keeps moving. The gap isn't just seeing the threat; it's acting on it fast enough to matter.
Refoundry MXDR closes that gap. We don't just detect threats on your Microsoft security stack. We own the response, from the moment an alert fires to the moment the attacker is contained.
The Agentic SOC, Powered by Security Copilot
Refoundry's Agentic SOC runs AI agents through the first and second shift of analyst work, so your team, and ours, spends time on judgment calls, not alert triage.
No rip-and-replace required. It fits directly into the Microsoft investment you already have and amplifies it with an agentic operating layer, built on:
- Microsoft Entra ID
- Microsoft Sentinel (SIEM)
- Microsoft Defender XDR
- Microsoft 365 E5
- Microsoft Security Copilot
Two Deployment Models
| Deployment Model | Best For | How it Works |
|---|---|---|
| Microsoft Security Copilot | E5 + SCU clients | Copilot drives investigation skills natively; SCU cost stays in your tenant. Refoundry runs the managed service on top. |
| Refoundry Agent Layer | Mid-market & SMB | Our own orchestrator routes each task to the right AI model for the job; AI cost is absorbed into the contract — no SCU required |
How Our AI Agents Triage and Investigate Incidents
L1 Agent: Autonomous Triage
The L1 agent runs on every Sentinel incident the moment it fires:
- Scores and correlates related signals
- Automatically suppresses known false positives
- Escalates real threats to the L2 agent with a pre-built brief
L2 Agent: Deep Investigation
Triggered by an L1 escalation, the L2 agent runs the full investigation toolkit:
- User investigation and scope-drift analysis
- IoC enrichment and authentication tracing
Produces a structured, decision-ready report for human review
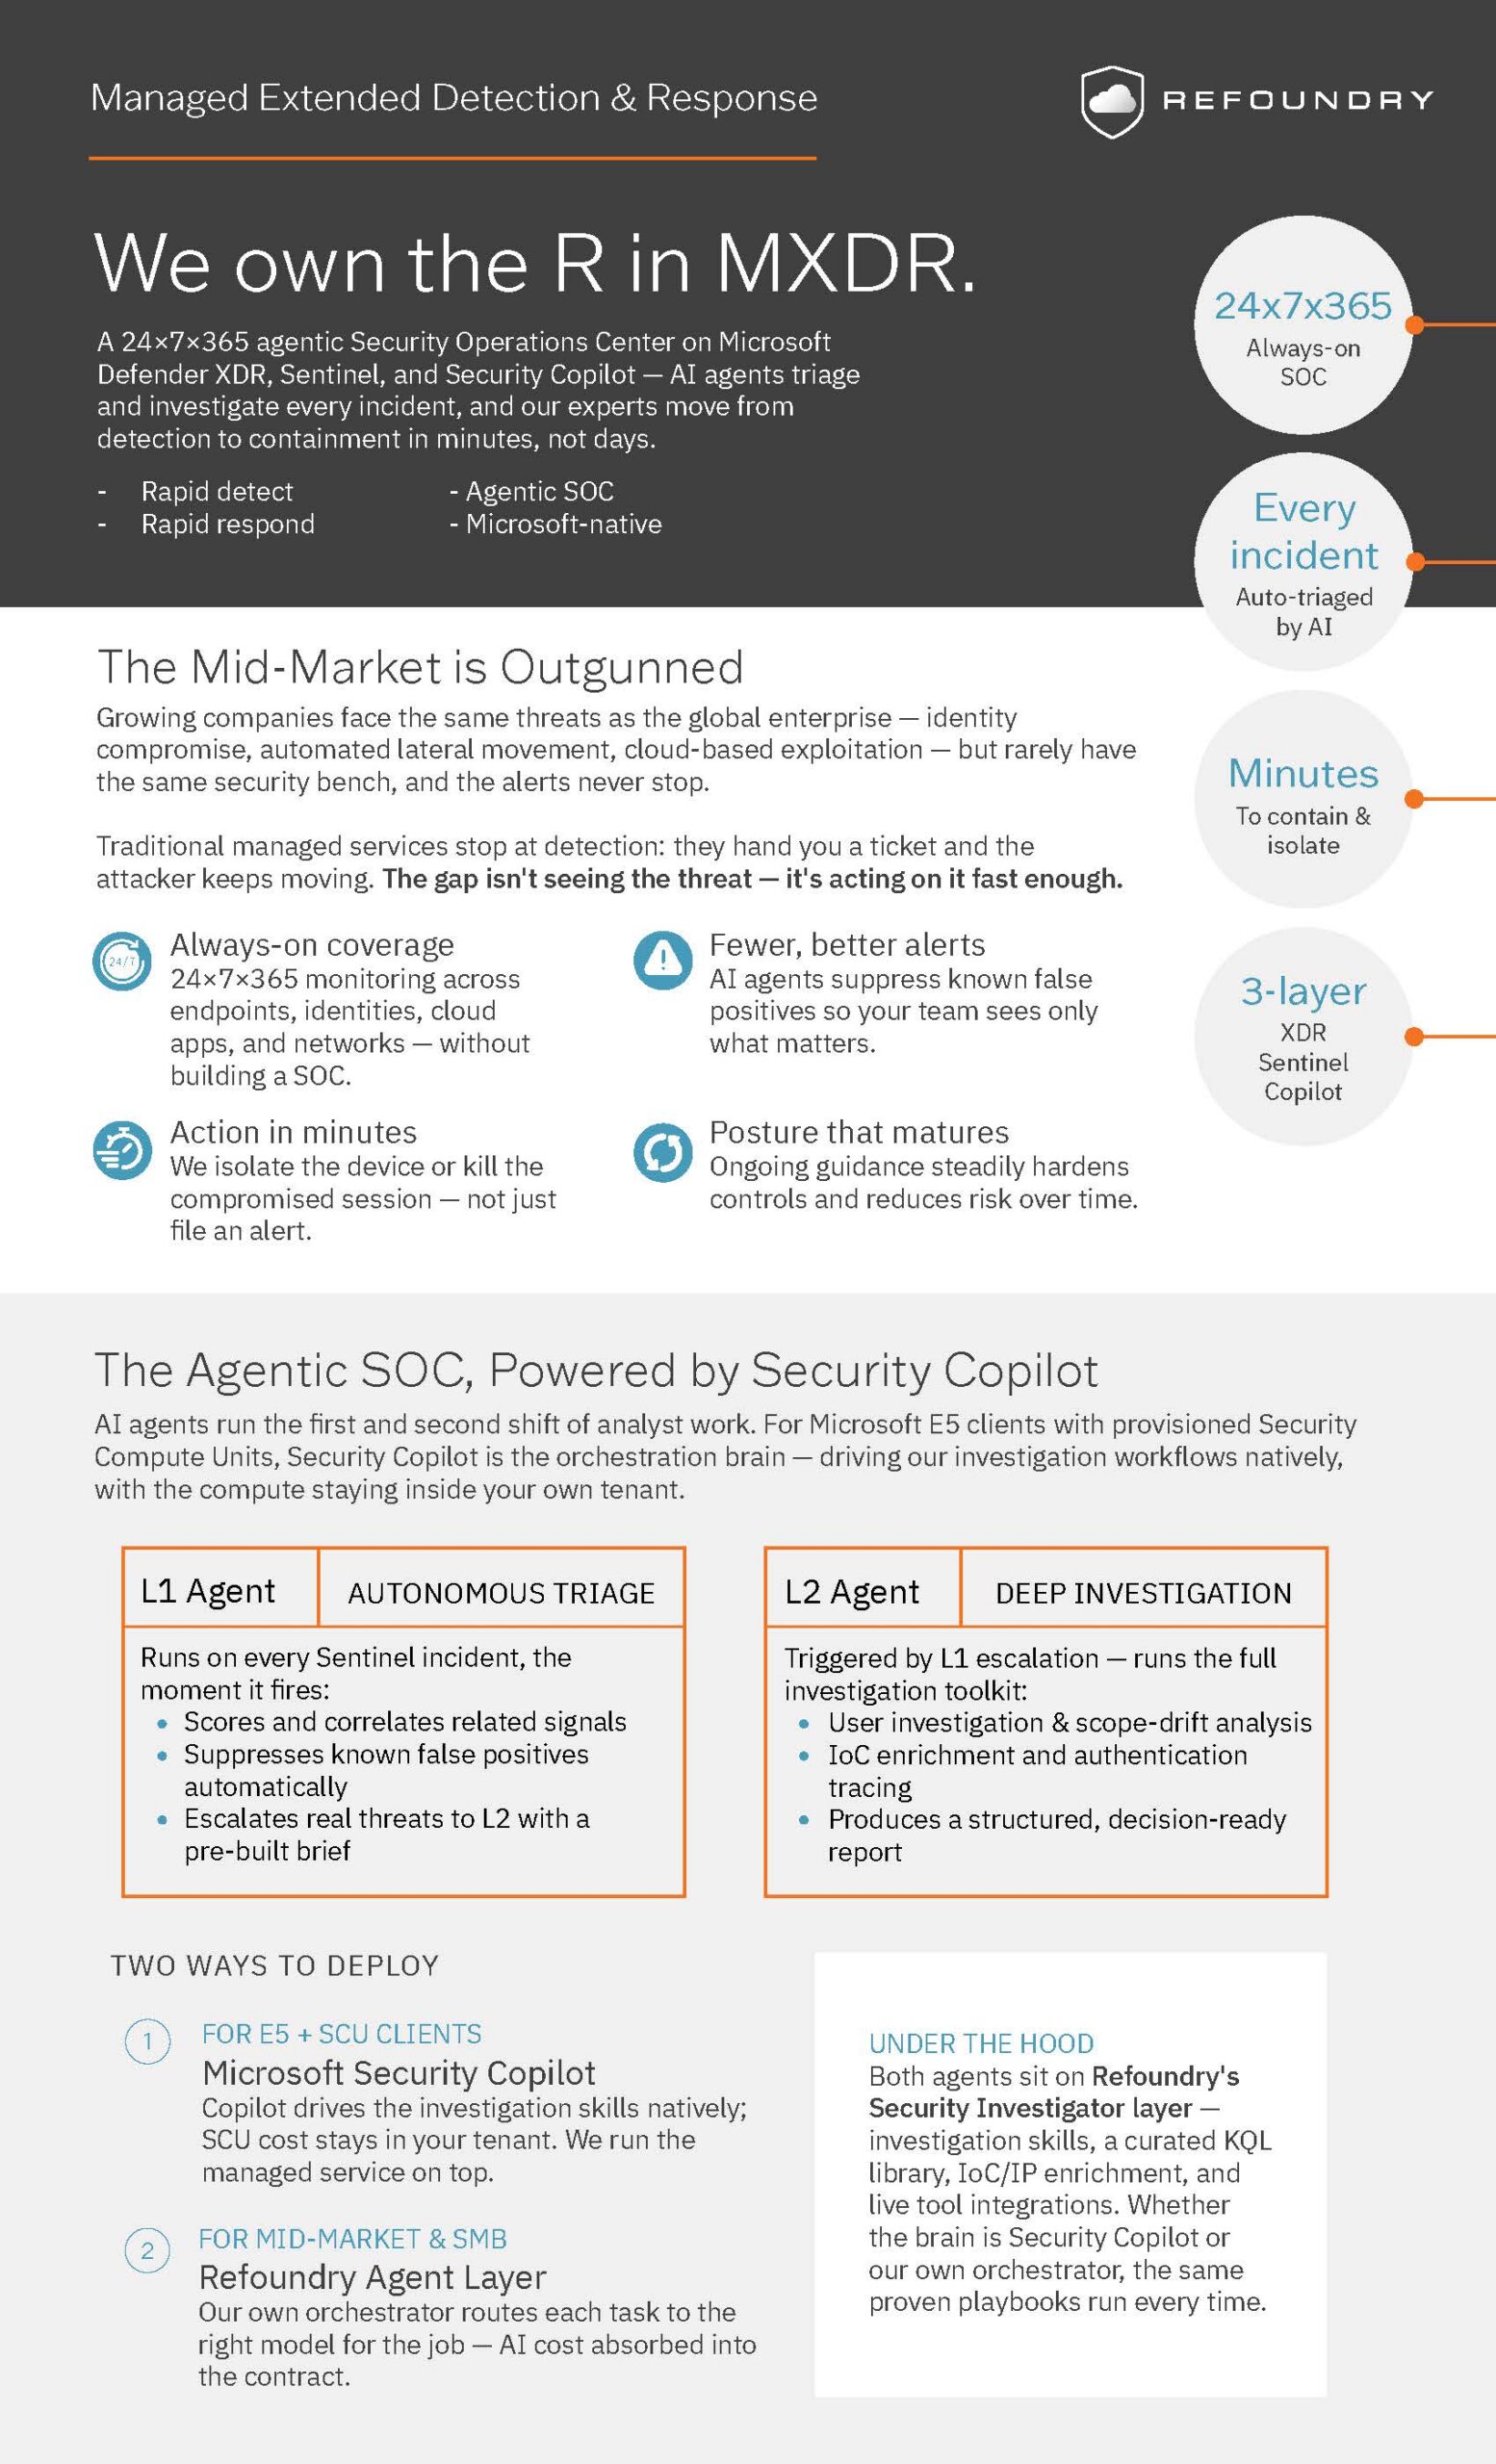
One managed service, covering detection through response:
- 24×7×365 Monitoring — Continuous coverage across endpoints, identities, cloud apps, and network telemetry.
- Agentic L1/L2 Triage — Autonomous scoring, correlation, false-positive suppression, and AI-led investigation.
- Security Copilot Orchestration — For E5 + SCU clients, Copilot drives investigations natively while compute stays in your tenant.
- Owned Response — Orchestrated revoke, reset, and isolate playbooks executed by our SOC — not a ticket back to your team.
- Proactive Threat Hunting — Hunting subtle signals like early lateral movement and anomalous logins before they escalate.
- Posture Guidance — Ongoing recommendations that harden controls and steadily reduce risk over time.
FAQ
Ready to Own Your Response?
Let's walk through how Refoundry MXDR plugs into your environment and how fast we get from alert to contained.
